

What are we working on?
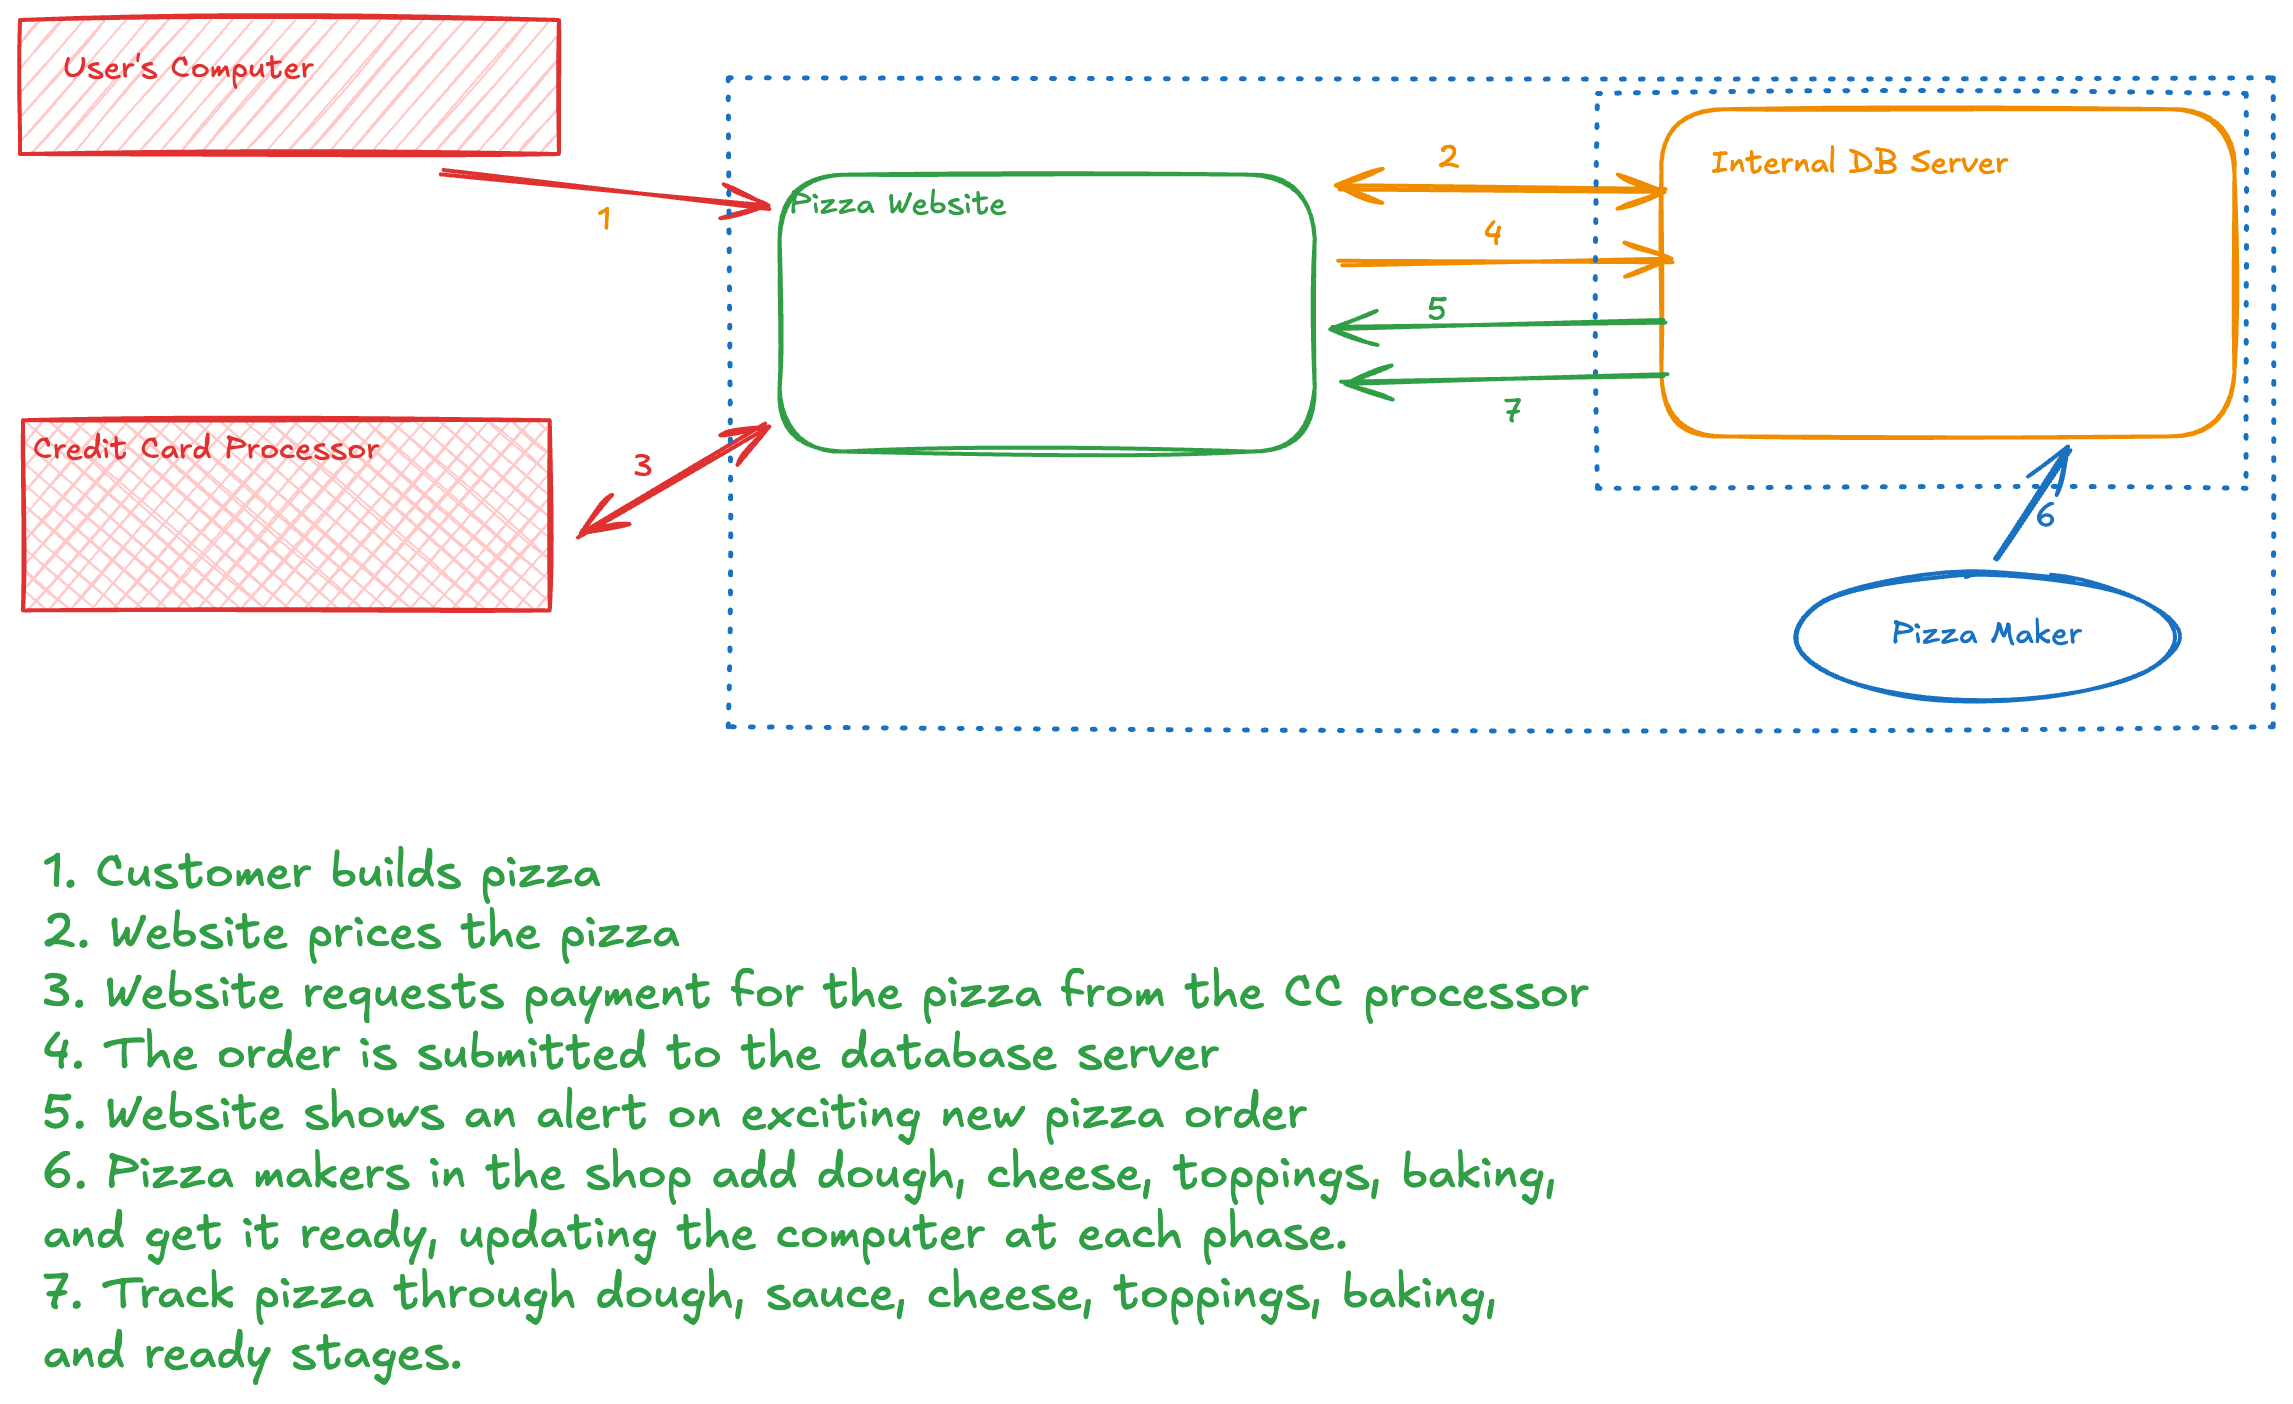
The project being reviewed is an online pizza restaurant. To help make the experience more engaging, it includes a social component where people can see what pizzas have been ordered and customers can track their pizza through the creation process. For simplicity, only credit cards are taken for payment, only one payment processor is used, and all pizza is picked up from the store (no delivery). The typical “happy path” flow includes:- The customer builds their pizza on the website from a list of ingredients.
- When finished building, the website calculates the price of the pizza by querying the database.
- The customer enters their payment information on the website and the website connects to the credit card processor to process the payment.
- The pizza order is added to the database.
- For the social component, once the order is in the database, it is also displayed on the starting page of the webpage with the user’s username.
- Pizza makers in the pizza shop check the database and begin building the pizza through various stations, including dough, sauce, cheese, toppings, baking, and boxing. One pizza worker is at each station.
- At each step, the pizza maker updates the database with current progress. As the database is updated, the pizza tracker on the website is updated, showing current progress and who has completed that step.
- Customer picks up their pizza once it is ready.
What can go wrong?
STRIDE reminders
Threat table
What are we going to do about it?
Did we do a good job?
-
Has the data flow diagram been referenced since it was created?
- Yes, it was invaluable in building the threat profile.
-
Did the STRIDE model uncover any new design issues or concerns that had not been previously addressed or thought of?
- Yes. We realized we needed to change the pizza station authentication scheme. Additionally, we reframed the queries for the pizza order social display to only deliver the needed information.
-
Did the treatments identified in the “What are we going to do about it” section adequately address the issues identified?
- Yes. We are continuing to monitor these in the event additional mitigations are needed.
-
Have additional issues been found after the threat model?
- None yet. As new features are added, the threat model will be updated to reflect the new additions.
-
Any additional thoughts or insights on the threat modeling process that could help improve it next time?
- None.